OrbletiQ / Advisory

Govern AI. Manage Risk. Build Trust.

Independent AI governance, technology risk and cybersecurity advisory for organisations navigating emerging technologies, complex control environments and evolving regulatory expectations.

AI Governance Technology Risk Assurance
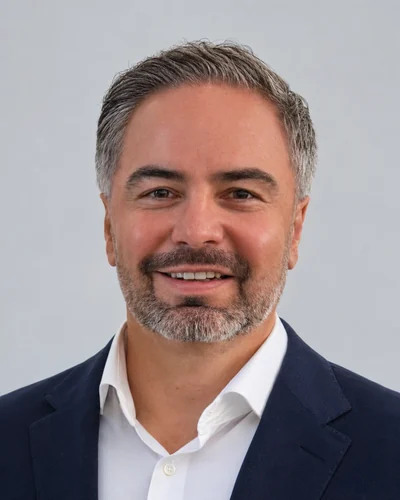
Łukasz Bugiera, Founder and Principal Consultant at OrbletiQ
Łukasz BugieraFounder & Principal Consultant

16+ years in internal audit, technology risk and cybersecurity in financial services

  • CIA
  • CISA
  • CISM
  • CRISC
View credentials →

16+ years of experience built at

JPMorganChase PwC MetLife International Personal Finance

The founder's previous employers. Logos are trademarks of their respective owners and do not imply endorsement of OrbletiQ.

Where we help

When AI adoption moves faster than governance

Organisations typically come to us when they recognise one of these situations.

We're introducing AI agents, but nobody has defined their operational boundaries.
We have AI policies, but no practical controls behind them.
We need to understand what ISO/IEC 42001 or the EU AI Act means for our operations.
We're not sure our existing IT controls are adequate for AI-based workflows.
Our internal audit function needs a practical methodology for auditing AI.
We need evidence that our technology controls are actually working.

How ready is your organisation to govern AI?

Explore your AI governance maturity through a short, structured self-assessment covering governance, security, risk management and regulatory readiness.

Check Your AI Readiness

Ways to work with us

Choose your starting point

Start by understanding your AI governance gaps, then design the processes and controls needed to address them. Focused engagements cover EU AI Act requirements, ISO/IEC 42001 readiness, lifecycle security, AI agent controls and audit preparation. Each engagement is available independently, with scope and outputs agreed before work starts.

AI Governance Gap Assessment

Who it is for
Risk, compliance, security and technology leaders who need an overall view of their organisation’s AI governance maturity and priorities.
The problem
AI adoption has moved faster than ownership, inventories and controls. Management lacks a consolidated view of the AI systems in use, how they are governed and where action is needed.
What the engagement covers
  • Inventory of AI systems and use cases in scope
  • High-level mapping of relevant regulatory, framework and sector expectations
  • Review of existing policies, roles, controls and evidence
  • Interviews with system owners, risk, compliance, IT and security
What you receive
  • AI system inventory with preliminary risk classification
  • Governance gap register with ratings and proposed owners
  • Prioritised remediation roadmap
  • Summary for management and the board

Potential next step: AI Governance & Intake Design to address the assessment findings.

AI Governance & Intake Design

Who it is for
Organisations acting on governance assessment findings or establishing a structured approach to AI ownership, intake and approval.
The problem
AI requests arrive through different channels, with unclear ownership and inconsistent reviews. Teams need practical governance that turns policy into accountable decisions and everyday processes.
What the engagement covers
  • Governance design informed by NIST AI RMF and ISO/IEC 42001
  • Governance roles, decision rights and escalation routes
  • Intake for internally developed AI, purchased tools and embedded AI features
  • Risk classification and routing to security, privacy, legal and compliance reviews
  • Approval criteria, exceptions and reassessment triggers
What you receive
  • AI governance operating model and responsibility matrix
  • AI intake questionnaire and use-case register template
  • Risk classification and approval workflow
  • Governance mapping to NIST AI RMF and ISO/IEC 42001
  • Implementation roadmap with prioritised actions

EU AI Act Regulatory Gap Assessment

Who it is for
Organisations developing, providing or deploying AI that need to understand their applicable EU AI Act obligations and current compliance gaps.
The problem
AI responsibilities depend on the organisation’s role, the system’s intended purpose and its risk classification. Teams need a clear view of applicable requirements, supporting evidence and outstanding actions.
What the engagement covers
  • AI systems in scope and the organisation’s regulatory roles
  • Applicability, prohibited practices and risk classification
  • Applicable obligations, implementation dates and transitional provisions
  • Existing governance, controls, documentation and evidence
  • Accountability and actions required to address identified gaps
What you receive
  • EU AI Act applicability and role assessment
  • Requirements-to-controls gap matrix
  • Gap register with evidence needs and proposed owners
  • Prioritised remediation roadmap aligned with applicable deadlines

ISO/IEC 42001 AIMS Readiness Review

Who it is for
Organisations establishing an AI management system (AIMS), improving an existing system or preparing for ISO/IEC 42001 certification.
The problem
AI policies and individual controls may exist without a coherent management system. Teams need to understand whether governance, risk management and assurance processes are sufficiently defined, implemented and evidenced.
What the engagement covers
  • AIMS scope, organisational context, leadership and responsibilities
  • AI risk and impact assessment processes
  • Control selection, Statement of Applicability and supporting documentation
  • Operational processes, objectives and performance monitoring
  • Internal audit, management review and continual improvement
What you receive
  • ISO/IEC 42001 readiness assessment
  • Management system and control gap register
  • Documentation and evidence checklist
  • Prioritised preparation roadmap

This review assesses readiness. It does not provide certification or guarantee a certification outcome.

AI Lifecycle Security & Compliance Review

Who it is for
Technology, security, risk and compliance teams developing, procuring, deploying or operating AI systems.
The problem
AI systems move from proposal to production without consistent security and compliance checkpoints. Teams need clear control requirements, evidence and accountable decisions throughout the lifecycle.
What the engagement covers

Review of controls and approval gates across eight lifecycle stages:

  1. AI Use-Case Registration & Risk Classification
  2. Pre-Release Security & Compliance Review
  3. High-Risk AI Authorisation
  4. Deployment Readiness & Control Verification
  5. Operational Monitoring & Incident Response
  6. Material Change Assessment
  7. Annual Governance & Control Review
  8. AI Retirement & Secure Decommissioning

A stage is a phase of the lifecycle. A gate sets the review, evidence and approval needed to move to the next stage.

Across applicable stages, we assess control requirements, ownership, supporting evidence and the conditions for progression.

What you receive
  • Lifecycle control and gate assessment
  • Gate matrix with evidence requirements and approval responsibilities
  • Prioritised findings and remediation plan with proposed owners
  • Recommendations for release, operation, change and retirement controls

AI Agent Controls Review

Who it is for
Organisations piloting or running AI agents that can call tools, access data or take actions in business systems.
The problem
Agents act with delegated authority, but their permissions, approval points, logging and stop mechanisms are often defined case by case, or not at all.
What the engagement covers
  • What each agent in scope can access and do
  • Authorisation and delegated-authority model
  • Human approval and oversight points
  • Logging, traceability and exception handling
  • Exposure to prompt injection and unsafe tool use
What you receive
  • Agent inventory and authority matrix
  • Rated findings with recommended actions
  • Agent control set mapped to your existing control framework

AI Audit Readiness

Who it is for
Internal audit functions planning AI audits, and first- and second-line teams preparing to be audited on AI.
The problem
AI is on the audit plan, but there is no agreed audit universe, test approach or evidence standard for AI systems. Control owners do not know what auditors will ask for.
What the engagement covers
  • AI audit universe and risk-based priorities
  • Test steps for AI governance, AI systems and AI agents
  • Evidence expectations for control owners
  • Walkthrough of selected controls against those expectations
What you receive
  • AI audit universe and risk assessment
  • Audit programme with test steps
  • Evidence checklist for control owners
  • Readiness findings and actions

Discuss your project

Example deliverables

What clients receive

Extracts from three typical outputs. The content is fictional and shows the format and level of detail only.

Illustrative example

AI risk and control matrix

IDRiskKey controlOwnerEvidence
R-01Customer chatbot gives inaccurate answers on product termsAnswers limited to an approved knowledge base; out-of-scope questions passed to a human agentHead of Customer ServiceMonthly sample review log
R-02Staff paste personal data into an unapproved AI toolApproved-tool list enforced at the web proxy; data loss prevention rule on uploadsCISOProxy configuration; DLP alert report
R-03Model performance degrades after deployment without anyone noticingDrift metrics with alert thresholds; scheduled revalidationModel ownerMonitoring dashboard; revalidation report
Illustrative example

AI agent authority matrix

AgentActs on its ownNeeds human approvalNot permittedAccountable owner
Invoice-matching agentMatches invoices to purchase orders within toleranceReleasing payments; changing supplier bank detailsCreating new suppliersAccounts payable process owner
IT service-desk agentResets passwords after identity check; opens ticketsAdding users to privileged groupsChanging firewall rulesIT service manager
Research assistant agentSearches approved internal sources; drafts summariesSending content outside the organisationAccessing HR or customer recordsHead of Strategy
Illustrative example

Prioritised remediation roadmap

  1. Priority 1 · first 3 months

    • Appoint an accountable owner for each AI system
    • Complete the AI system inventory
    • Stop use of unapproved AI tools for personal data
  2. Priority 2 · months 3 to 6

    • Introduce an approval gate for new AI use cases
    • Apply a logging standard to all AI agents
  3. Priority 3 · months 6 to 12

    • Add AI controls to the annual control testing plan
    • Report AI risk to the board each quarter

Capabilities

Areas of expertise

The engagements above draw on four areas. Expand each to see the detailed capabilities.

AI Governance & Regulatory Alignment

Ownership, policies and controls for AI, aligned with the EU AI Act, ISO/IEC 42001 and sector requirements.

Capabilities
  • AI governance operating models
  • AI policies, standards and procedures
  • AI risk classification and inventories
  • Lifecycle governance and human oversight
  • EU AI Act, DORA and NIS2
  • ISO/IEC 42001 and ISO/IEC 27001
  • NIST AI RMF and COBIT
  • GDPR-related technology governance

Technology Risk & Cybersecurity

Identify, assess and manage technology and security risks, with a focus on real risk reduction.

Capabilities
  • Cybersecurity risk assessments
  • ITGC and ITAC design and evaluation
  • Identity and access management controls
  • Cloud, infrastructure and third-party risk
  • Resilience and remediation planning
  • Financial-services supervisory expectations

Internal Audit & Independent Assurance

Risk-based advisory and assurance support for internal audit functions and leadership.

Capabilities
  • Risk-based audit planning
  • IT, cybersecurity and AI governance audit
  • Control design and operating effectiveness
  • Control testing methodologies
  • SOX technology controls; SOC 1 / SOC 2 readiness
  • Audit methodology and reporting

OrbletiQ provides governance, risk, controls and implementation advisory. We do not provide legal opinions, formal attestations, certification or statutory audit services; readiness assessments are designed to prepare you for those processes.

Why OrbletiQ

Where technology expertise meets independent risk judgement

Many AI consultancies focus on implementing technology. Traditional assurance often focuses on policies and compliance. We connect the two.

Technology

Enterprise IT, cybersecurity, infrastructure, cloud and AI architectures — and how they actually operate.

Risk & Assurance

Governance, risk management, control effectiveness, audit evidence and executive oversight.

Emerging AI

The new governance challenges of generative AI, autonomous agents and multi-agent systems.

Practical over theoreticalFrameworks designed to be implemented and operated — governance that works beyond the policy document.
Risk-based, not checklist-drivenControls proportionate to the risks that genuinely matter.
Independent judgementRecommendations based on professional expertise, not on selling particular AI platforms.
Technical depth, executive clarityComplex issues made understandable for management and boards.
Governance that enables innovationAppropriate oversight without unnecessary bureaucracy.
Founder-ledDirect access to an experienced senior professional, not an unspecified delivery team.

Approach

From complex requirements to controls that work

Effective governance is not about producing more documentation. It is about understanding what can go wrong and making sure the right controls stay effective as technology changes.

Understand

What can go wrong: your technology, AI use, data, obligations and existing control environment.

Prioritise

Which risks matter, with clear ownership and accountability for each.

Design

Proportionate, testable controls and governance that fit how your organisation actually works.

Sustain

Monitoring, testing and reporting so controls remain effective as technology evolves.

Frameworks we work with

EU AI ActISO/IEC 42001NIST AI RMFDORANIS2ISO/IEC 27001COBITGDPRMaRisk / BAIT

About OrbletiQ

Built on experience. Focused on what's next.

AI systems increasingly make recommendations, take actions, connect to corporate information and participate in complex workflows. Traditional governance, cybersecurity and audit methodologies do not always address the distinctive challenges this creates — and governance advice is too often theoretical, producing documents that are hard to implement.

OrbletiQ was established to close that gap. Our mission is to turn complex technology and AI governance requirements into practical, proportionate, testable and sustainable controls — so organisations can adopt new technology confidently while maintaining accountability, transparency and human oversight.

“I founded OrbletiQ to bring the discipline of assurance and internal control to emerging AI — in a form organisations can actually operate. Good governance should enable responsible innovation, not slow it down.”
— Łukasz Bugiera, Founder & Principal Consultant

Based in the Warsaw area, we work with organisations across Poland, the European Union and internationally, in English and Polish. Our focus is on mid-sized and large organisations in banking, insurance and other regulated or risk-sensitive sectors, as well as enterprises adopting AI and automation at scale.

Founder experience and credentials →

Contact

Discuss your project

Tell us briefly about your organisation and what you are working on. You will hear back directly from Łukasz, usually within one business day.

Email
[email protected]
Location
Józefów, Warsaw area, Poland
Languages
English, Polish
LinkedIn
Łukasz Bugiera

Fields marked are required.

Your details are used only to respond to your enquiry. See our privacy notice.